
 Kontakt
 Ako nakupovať

Doručenie
Nákupný poradca
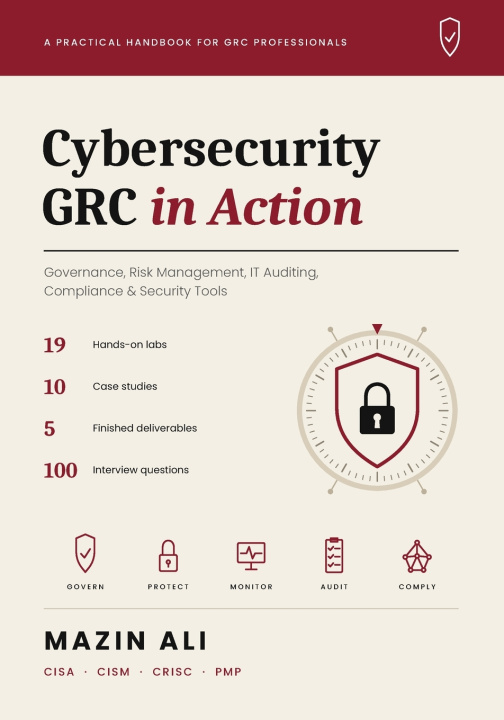
Cybersecurity GRC in Action
The Practical Handbook for Governance, Risk Management, IT Auditing, Compliance & Security Tools
 Angličtina
 39 b
 Pripravujeme
 Nové
Až 30 dní na vrátenie tovaru

Learn cybersecurity GRC the way it's actually done on the job, with hands-on labs, real deliverables, and practical guidance on the tools employers use.
Most cybersecurity books explain frameworks. This one shows you how to use them. You'll follow one organization through the full GRC cycle, from scoring a risk to testing the control, monitoring it, and reporting it to the board, and finish with professional work products you can model your own on.
Written by a cybersecurity GRC professional who holds the CISA, CISM, CRISC, CompTIA Security+, CompTIA CySA+, and PMP certifications, with a background in accounting and financial controls.
Inside you'll find:
- 19 hands-on labs: run a risk assessment, quantify a risk with a simple loss simulation, test a control from walkthrough to conclusion, write an audit report, perform a SOC 2 readiness assessment, and more
- 10 detailed case studies across banking, healthcare, defense, SaaS, retail, manufacturing, insurance, education, payroll, and public companies
- 5 complete professional deliverables: an internal audit report, a SOC 2 gap assessment, an access control policy, a monitoring specification, and a risk-acceptance form
- 22 templates and 25 exercises with answer keys
- 100 interview questions with model answers for GRC, IT audit, and risk roles
Topics covered:
NIST CSF 2.0 · NIST SP 800-53 · ISO/IEC 27001 · CIS Controls · COBIT · risk management · IT auditing and SOX ITGCs · SOC 2 · PCI DSS · HIPAA · CMMC · FedRAMP · third-party risk · board reporting · AI governance
Learn how GRC platforms and Splunk support compliance: you'll design risk registers, workflows, and dashboards and write Splunk searches for audit evidence. The Archer and ServiceNow material teaches the concepts in a vendor-neutral way; it doesn't walk through specific product screens.
Perfect for:
- Aspiring GRC analysts and IT auditors
- Security professionals moving into risk and compliance
- Accounting and finance professionals entering cybersecurity
- Anyone preparing for GRC job interviews
Current as of 2026, including CSF 2.0, the latest CMMC phase-in, and the SEC cyber disclosure rule.
Scroll up and get your copy today.
This book is not affiliated with or endorsed by ISACA, CompTIA, PMI, NIST, ISO, Archer, ServiceNow, Splunk, or any other organization named.


Informácie o knihe
Angličtina

Darujte túto knihu ešte dnes
Je to jednoduché
1 Pridajte knihu do košíka a vyberte možnosť doručiť ako darček 2 Obratom Vám zašleme poukaz 3 Knihu zašleme na adresu obdarovanéhoAhoj! Som Libroamiko, tvoj knižný radca.
Ako ti môžem pomôcť?